SCIF vs SAPF: Key Differences in Secure Government Facilities
In government and defense environments, not all secure facilities are created equal. Programs handling classified information must operate within highly controlled environments that meet strict physical, technical, and accreditation requirements. Two of the most common secure environments are Sensitive Compartmented Information Facilities (SCIFs) and Special Access Program Facilities (SAPFs).
While SCIFs and SAPFs share similar security foundations, their purpose, access controls, and accreditation requirements differ in critical ways. Understanding the distinction between SCIF vs SAPF is essential for military personnel, government agencies, and defense contractors responsible for protecting classified information and mission‑critical programs.
This guide explains the differences, use cases, and considerations to help organizations determine the right secure facility for their mission.
What Is a SCIF (Sensitive Compartmented Information Facility)?
SCIF Definition and Purpose
A SCIF is a secure facility designed to store, process, discuss, or transmit Sensitive Compartmented Information (SCI). SCI is classified intelligence that requires handling beyond standard classified information controls.
The primary purpose of a SCIF is to prevent unauthorized access, espionage, electronic surveillance, or accidental disclosure of national security information. Under ICD 705, SCI must be stored, processed, used, or discussed within an accredited SCIF.
SCIF Security Standards and Requirements
SCIFs must comply with strict federal security standards, including the ICD/ICS 705 series and the National Counterintelligence and Security Center (NCSC) Technical Specifications for Construction and Management of SCIFs, which establish baseline construction and security requirements. However, the Accrediting Official (AO) may impose additional measures based on the threat environment.
Technical Security: TEMPEST countermeasures (as required based on Certified TEMPEST Technical Authority (CTTA) review and AO determination), protection against electronic eavesdropping, and secure communications infrastructure
SCIFs support secure briefings, intelligence analysis, data processing, and classified collaboration.
What Is a SAPF (Special Access Program Facility)?
SAPF Definition and Purpose
A SAPF is a secure facility designed to support Special Access Programs (SAPs). SAPs involve exceptionally sensitive projects where access is restricted beyond standard clearance levels.
SAPFs are governed by program‑specific security requirements, and use SCIF standards as a baseline while incorporating additional program-specific controls and restrictions.
SAPF Security Requirements and Access Controls
While SAPFs share many baseline physical and technical security elements with SCIFs, they typically include:
Program‑Specific Access Controls: Access limited strictly to personnel with explicit SAP approval, even within an existing SCIF
Enhanced Security Measures: Additional controls such as compartmentalized layouts, enhanced acoustic or technical protections, and TEMPEST countermeasures based on program requirements and threat assessments
Heightened Oversight: Direct control by program authorities with limited visibility outside the SAP
SAPF Use Cases in Defense Programs
SAPFs are commonly used for:
Advanced weapons development
Classified aerospace or cyber programs
Highly sensitive R&D efforts
These facilities ensure that information is only accessible to individuals with both clearance and explicit need‑to‑know.
SCIF vs SAPF: Key Differences Explained
Feature
SCIF
SAPF
Primary Purpose
Protect SCI
Project special access program information/activity
SAPF Accrediting Official / SAP security authority
Security posture
Risk-based secure facility controls
Baseline secure-facility controls plus program-specific restrictions
Accreditation and Oversight
Both SCIFs and SAPFs require formal accreditation. SCIFs are governed by the ICD/ICS 705 framework and NCSC Technical Specifications, while SAPFs follow DoD SAP security guidance (e.g., DoDM 5205.07) in addition to SCIF standards.
Final requirements are determined by the Accrediting Official based on:
Threat environment
Mission sensitivity
Risk tolerance
There is no one‑size‑fits‑all approach.
Physical and Technical Security Considerations
Some programs require:
TEMPEST countermeasures based on CTTA review and mission requirements
Advanced acoustic protections for amplified audio environments
Specialized engineering solutions to mitigate unique threats
These requirements must be incorporated into facility design from the beginning to ensure timely accreditation.
Can a Facility Be Both a SCIF and a SAPF?
Yes. In some cases, a SAPF may be located within a larger SCIF, when approved by the appropriate accrediting authorities and when additional program-specific controls and access restrictions are implemented.
Challenges of Maintaining Accredited Secure Facilities
Operating SCIFs and SAPFs presents ongoing challenges, including:
Evolving Compliance Requirements: Security standards must adapt to an ever‑changing threat landscape
Operational Costs: Upgrades, inspections, and re‑accreditation requirements
Personnel Training: Continuous training to maintain compliance and prevent security incidents
Organizations must carefully balance mission needs, risk tolerance, and long‑term costs.
How CenCore Supports SCIF and SAPF Requirements
CenCore specializes in designing, building, and securing accredited SCIFs and SAPFs for government and defense customers.
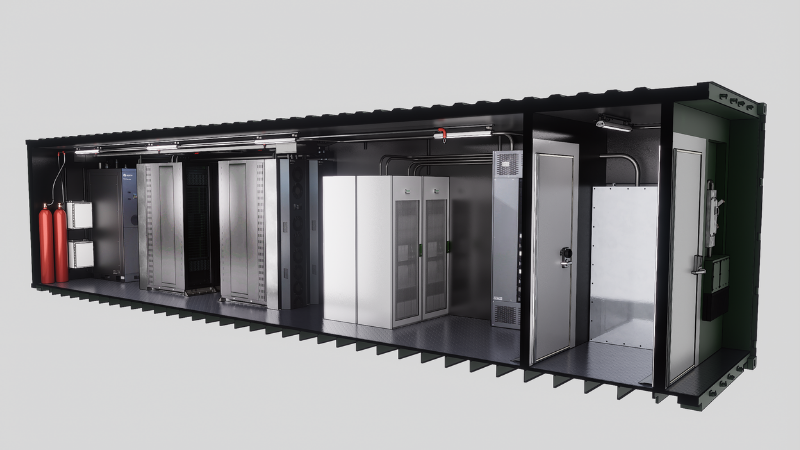
Our Containerized Secure Units (CSUs), often referred to as SCIF in a Box, provide:
Rapid deployment
Scalable and modular designs
Compliance with physical security, acoustic, and TEMPEST requirements
Solutions tailored to the Accrediting Official’s specific risk profile
CenCore designs and builds solutions including SCIFs, SAPFs, and other secure platforms that support accreditation in alignment with Accrediting Official requirements and mission needs.
Learn more about ourSCIF Platformsand how they support classified operations.
Frequently Asked Questions About SCIFs and SAPFs
A SCIF protects Sensitive Compartmented Information (SCI), while a SAPF supports Special Access Programs with additional access restrictions and security requirements.
Organizations that store, discuss, process, or transmit SCI need an accredited SCIF. Organizations supporting Special Access Programs may need a SAPF or a co-used arrangement approved by the relevant authorities.
Military units, government agencies, and defense contractors handling classified or SAP‑level information.
Yes, secure facilities may include mobile platforms, prefabricated structures, containers, and modular applications. But they are not automatically accreditable just because they are marketed that way; the Accrediting Official still determines whether the final design and controls meet the mission and threat requirements.
What Is a Micro Data Center and How Does It Reduce Reliance on the Power Grid?
Data processing does not always need to happen inside a large, traditional data center. There is an increasing need for computing infrastructure closer to where data is generated and used. A micro data center, like CenCore’s TRIDENT and STRIDE solutions, provides a compact way to establish compute capacity without relying on centralized data centers. A […]
Physical Security
6 min read
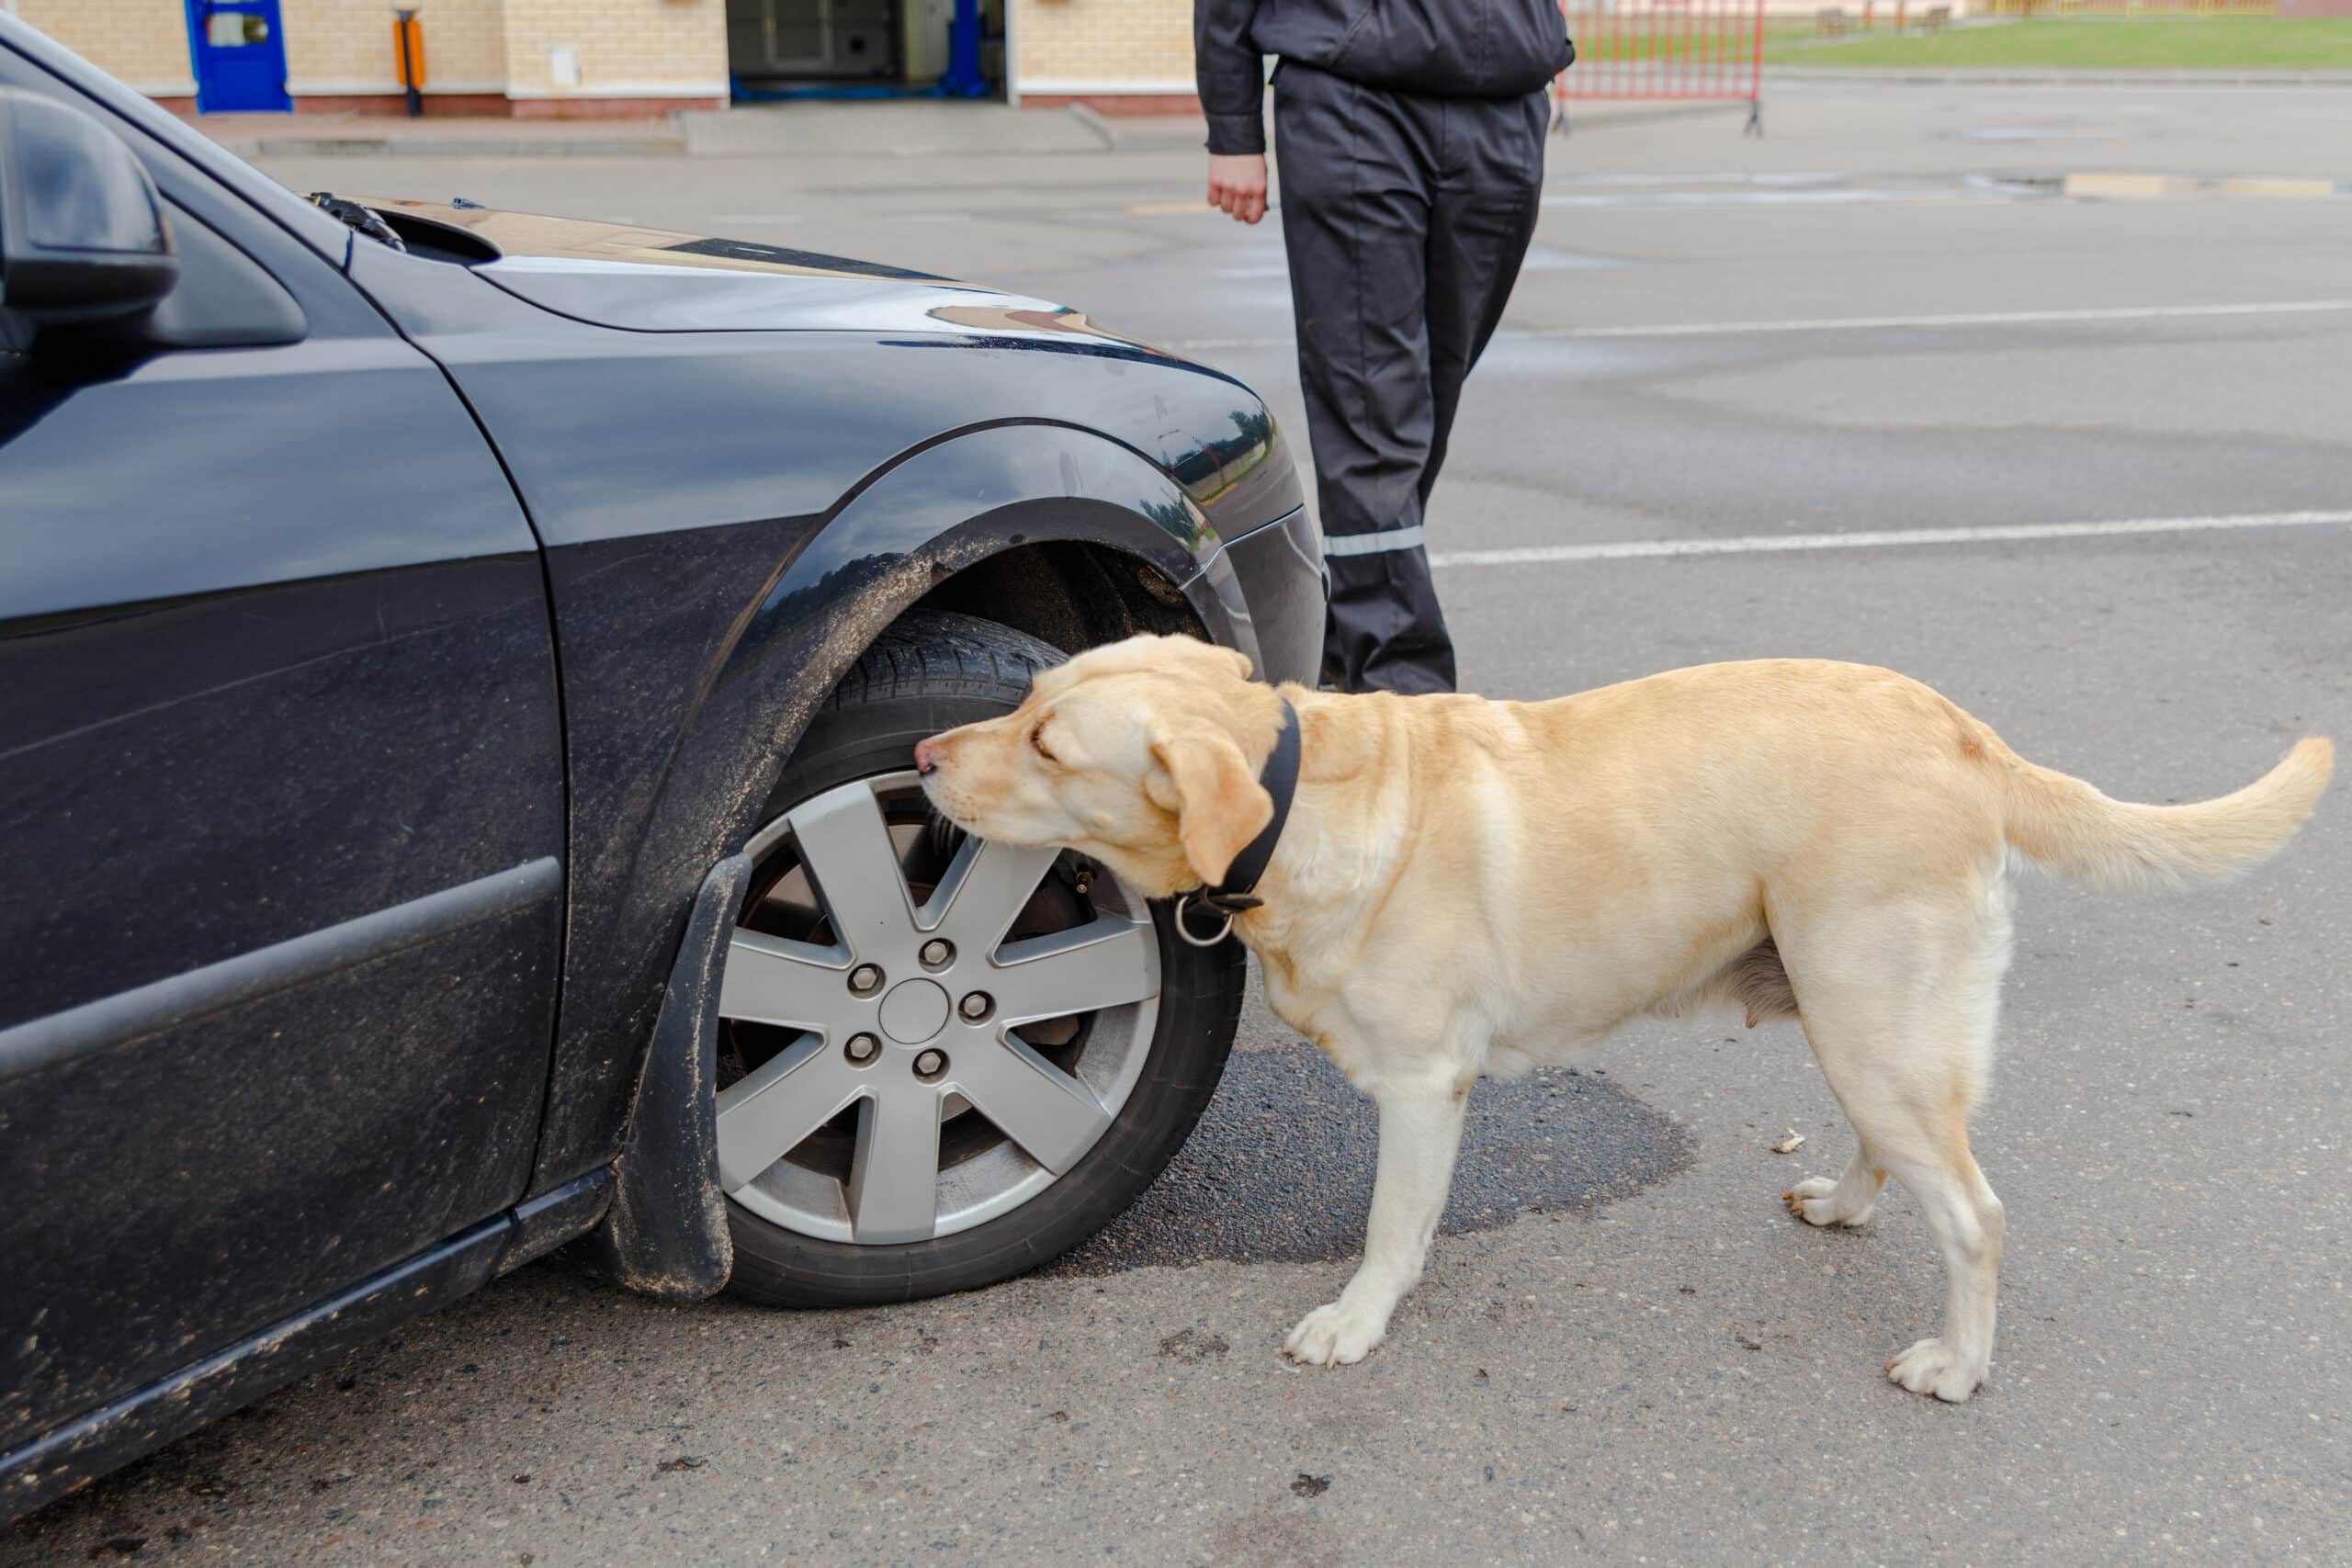
How Explosive Detection K9s Help Protect Critical Infrastructure
Government facilities, secure campuses, secure construction projects, and other high-value locations face evolving security challenges that demand rapid and effective threat detection. This is why CenCore explosive detection K9 teams remain one of the most reliable tools available for identifying potential threats before they can impact personnel, secure facilities, or operations. Highly trained detection dogs […]
Press Release
1 min read
LEMA Founder Brian Plourde Discusses Building Stronger Defense Partnerships
Founder and CEO Brian Plourde of LEMA joined us to talk about autonomous power generation, supporting the warfighter at the edge, and the realities of building capabilities for the defense industry. LEMA is focused on reducing logistics and manpower requirements through autonomous power generation. Brian discusses supporting systems such as SCIFs, data centers, and robotic […]